


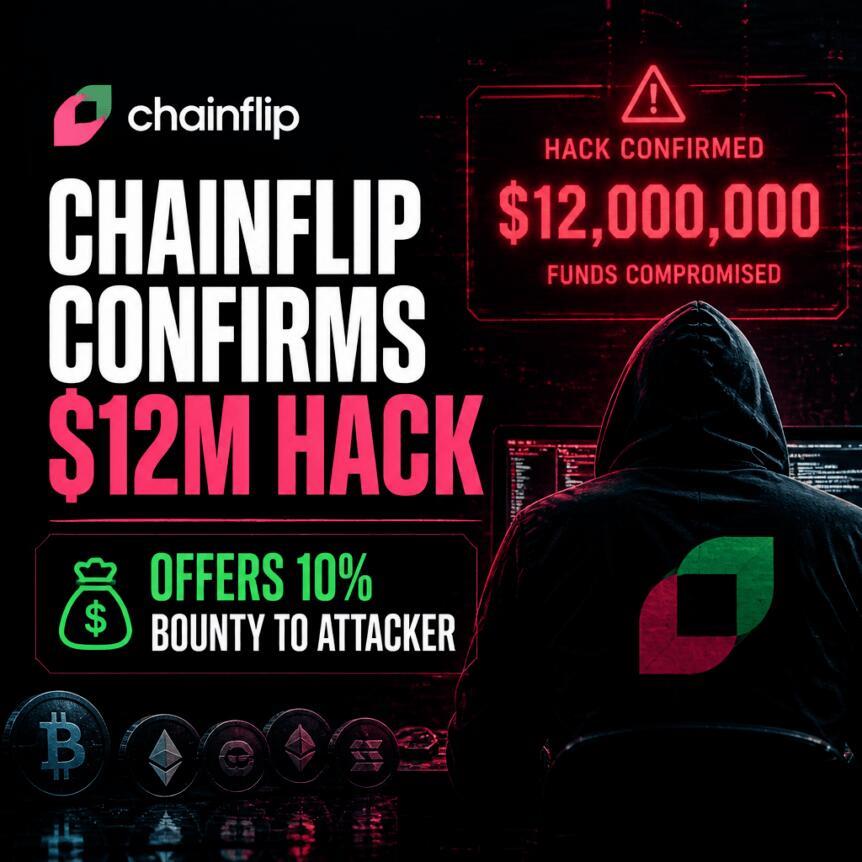
Chainflip Confirms $12M Hack, Offers 10% Bounty To Attacker


In its message to the attacker, Chainflip Labs said the stolen funds total 122.86 BTC, 520.22 ETH, 3.25 million USDC, and 758,141 USDT. The protocol operates cross-chain swaps, meaning vault security is central to user trust-especially when multiple assets and blockchains are involved in the same workflow.
Key takeaways- Chainflip confirmed the Saturday theft totals about $12 million, including BTC, ETH, USDC, and USDT. Chainflip is offering a 10% bounty for returning the remaining 90% of stolen assets by 18:38 UTC on Nov. 23. The protocol says it traced parts of the attack setup to Tornado Cash funding on Nov. 11 and a validator account created on Friday. Chainflip reports it identified the cryptographic key exposure mechanism and claims it has implemented safeguards to prevent similar incidents. Chainflip's FLIP token fell 42.9% over the past 24 hours, according to CoinGecko.
Chainflip's statement is directed at the attacker, asking for a return of the remaining stolen assets. The protocol proposed a structure in which 10% of the remaining funds would be paid as a bounty if the attacker returns 90% by 18:38 UTC on Nov. 23.
Chainflip also said it would treat any return as a“white-hat recovery.” It added that if funds are returned before the stated deadline, it would withdraw reports and complaints it had made to law enforcement, framing the offer as an incentive to unwind the theft without further legal escalation.
What was taken from the vaultsChainflip's confirmation provides specific balances across the main asset classes involved in the cross-chain environment:
- Bitcoin: 122.86 BTC Ether: 520.22 ETH USDC: 3.25 million USDC USDT: 758,141 USDT
While the statement does not detail the exact breach timeline or how the stolen assets moved after the initial exploit, the inclusion of both primary cryptocurrencies (BTC and ETH) and stablecoins suggests the attacker likely targeted liquidity-ready holdings within the vaults rather than limiting themselves to a single chain or asset type.
Chainflip's account of the attack setupAccording to Chainflip, it has traced preparation for the attack to Tornado Cash funding on Nov. 11 and to a validator account registered on Friday. The protocol said these two elements helped it narrow down the sequence of events leading to the theft.
Chainflip also claims it has identified the underlying“mechanism behind the cryptographic key exposure,” and says it has already taken steps intended to prevent the same class of attack from being repeated. For investors and users, that matters because cross-chain protocols rely on secure key handling and robust operational safeguards-an issue that, when it fails, can quickly turn into direct asset loss.
Message to the attacker and implications for enforcementChainflip used the statement to highlight what it says it knows about the attacker's identity and operational footprint. The company asserted it holds identifying information tied to the validator and servers used, and that the attacker's addresses are“flagged across every major analytics firm.”
It further stated that it is monitoring Tornado Cash withdrawals, implying ongoing tracking even if funds have already moved through privacy infrastructure.
This kind of public acknowledgment is often aimed at both deterrence and recovery. It also signals that Chainflip believes authorities and tracing partners may be able to connect the dots between on-chain activity and identifiable infrastructure.
Earlier coverage from Cointelegraph noted that a separate incident tied to the Binance hacker involved routing funds through THORChain and Chainflip, underscoring how cross-chain ecosystems can become part of wider capital flows during major hacks. In that broader context, Chainflip's disclosure of specific amounts and its enforcement-oriented message may be intended to reduce ambiguity around what happened and what the company is doing next.
Market reaction and what to watch nextThe reported incident is already showing up in Chainflip's token market. CoinGecko data shows Chainflip's FLIP token fell 42.9% over the past 24 hours, reflecting investor concerns about security risk and protocol operations.
What readers should watch in the coming days is whether the attacker accepts Chainflip's recovery terms before 18:38 UTC on Nov. 23, and whether further technical details emerge about the cryptographic key exposure mechanism. If Chainflip's mitigation steps hold, the protocol may recover some confidence-but until then, market participants are likely to focus on vault resilience, validator security, and the effectiveness of monitoring across privacy-related routes.
Risk & affiliate notice: Crypto assets are volatile and capital is at risk. This article may contain affiliate links.
Legal Disclaimer:
MENAFN provides the
information “as is” without warranty of any kind. We do not accept any
responsibility or liability for the accuracy, content, images, videos,
licenses, completeness, legality, or reliability of the information
contained in this article. If you have any complaints or copyright issues
related to this article, kindly contact the provider above.


Comments
No comment