


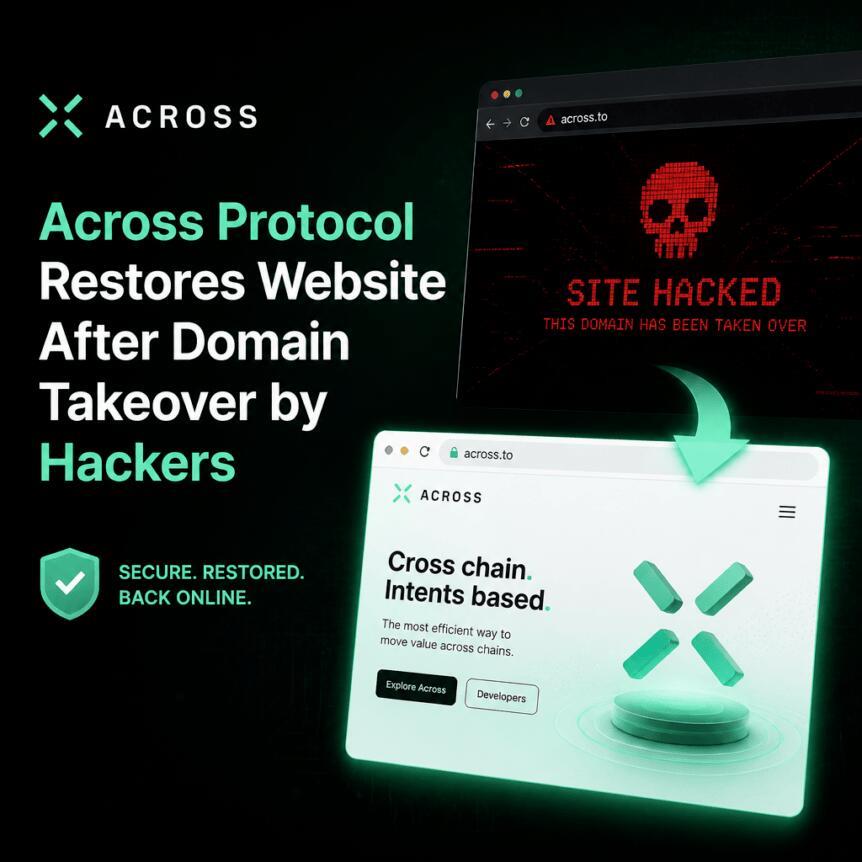
Across Protocol Restores Website After Domain Takeover By Hackers


In an update posted Wednesday, Across confirmed that the across domain is back under its control, with support from Namecheap founder Richard Kirkendall. The team added that its“systems are now working normally.” It did not disclose the total losses or how many users were impacted.
Key takeaways- Across reports its website is back online after attackers briefly redirected the across domain to a phishing page. The incident began after social engineering at Across's domain registrar, according to the bridge team's prior status update. Across says it will make affected users whole, but the amounts and scope have not been published yet. The team stated that third-party integrations and API users were not impacted. Across is one of the largest cross-chain bridges by transfer activity, per DefiLlama.
Across traced the disruption to an earlier event on Tuesday, saying a social engineering attack on its domain registrar (Namecheap) resulted in an attacker gaining control of its domain at around 18:45 UTC. In a separate update, the team said it was notified within 15 minutes and moved quickly to shut down the website to reduce further exposure.
The response effort involved multiple security and infrastructure players. Across said the security response group SEAL911 helped flag the domain as a phishing risk with major wallets. It also reported that Cloudflare marked the domain as at risk and later removed its DNS records-steps intended to limit further traffic to the malicious content.
Across also cautioned that some users could have been affected if they visited the domain before the malicious site was fully blocked.
What users may have faced-and what was sparedWhile Across did not provide specific details about which user actions were targeted or how many wallets were compromised, it framed the incident as a domain-level threat rather than a direct breach of its bridge infrastructure.
Importantly, the team said that third-party integrations and API users were unaffected. That distinction matters for traders and operators who rely on bridge-related services through automated systems: it suggests that the underlying cross-chain operations were not compromised by the website takeover itself, even though end users navigating via a browser may have encountered the phishing page.
Across also aligned with broader warnings that were issued soon after the incident began. Earlier coverage from Cointelegraph noted that Across urged users to avoid its app amid reports of drained wallets, though the bridge team later did not disclose totals related to the incident in this update.
Across's scale raises the stakes for phishing eventsThe operational impact of a phishing domain is amplified by user volume and trust-especially for bridges that facilitate large transfers between networks. Across is described as one of the most active cross-chain bridges by transaction and transfer metrics.
According to DefiLlama, Across ranked third by 30-day transfer volume, trailing Circle and LayerZero. Over that period, DefiLlama data cited by Across places the bridge at about $5.9 billion processed.
For investors and active users, that scale means a short-lived phishing replacement can have outsized consequences. Even if the window of exposure is brief, bridges with high usage tend to have correspondingly large numbers of users who may interact with the web interface or follow links from search results, bookmarks, or shared content.
Restoration and compensation: what to watch nextAcross says it regained control of its website with assistance from Richard Kirkendall and that its systems are now back to normal. The team also stated that it will compensate users who were affected, adding that it plans to share a“full post-mortem” in the coming days.
Until that post-mortem is published, several details remain unknown: the precise number of impacted users, the extent of any financial losses, and the practical timeline of when the domain was redirected and when protective measures fully took effect. For the broader community, the next key signal will be how Across documents the incident and what steps it says were implemented to prevent a repeat-particularly around registrar access, domain security controls, and how quickly customers can verify legitimate domains during emergencies.
As those details emerge, users who interact with bridge tooling should also keep in mind that domain-level phishing incidents can occur independently of bridge contract security-and the fastest path to safety is verifying URLs carefully and avoiding unexpected prompts or redirected pages, even during high-volume market activity.
Risk & affiliate notice: Crypto assets are volatile and capital is at risk. This article may contain affiliate links.
Legal Disclaimer:
MENAFN provides the
information “as is” without warranty of any kind. We do not accept any
responsibility or liability for the accuracy, content, images, videos,
licenses, completeness, legality, or reliability of the information
contained in this article. If you have any complaints or copyright issues
related to this article, kindly contact the provider above.


Comments
No comment