


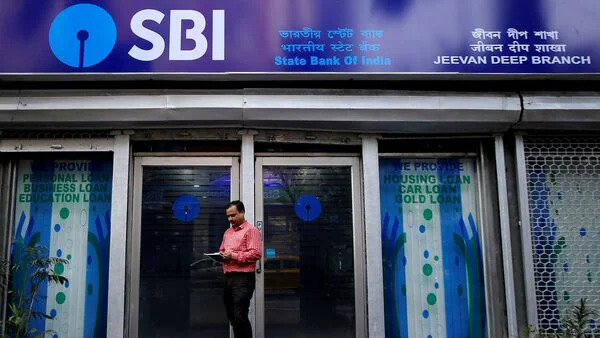
SBI Data Leak: This Is What India's Largest Public Sector Bank Told Customers As 3,897 Records Flagged In Cyber Incident


“Further to our earlier post regarding the recent cyber incident, the Bank has individually informed all customers, whose data was identified as being involved, through email and/or WhatsApp,” SBI said in an advisory to customers on Friday.
The bank reiterated that“your account balances and funds are safe with us” and urged customers to remain alert while using digital banking services.
Also Read | Good news! DA hike gift ahead of Diwali for government employees of this state SBI data leak: What information may have been exposed?In its advisory, SBI asked customers to exercise caution when handling sensitive banking information.
“Customers are advised to follow safe digital banking practices, never share their OTP, PIN or password with anyone, and remain vigilant against suspicious calls, messages and emails,” the advisory said.
The communication follows the bank's disclosure of a suspected data leak involving customer records reportedly found on the dark web.
According to SBI's stock exchange filing, a preliminary examination of around 3.75 lakh records identified 3,897 records containing personally identifiable information.
Also Read | ₹10,000 monthly in Post Office RD vs PPF: Returns compareThe information reportedly included customers' names, registered mobile numbers, dates of birth, email IDs and residential addresses. The records also contained branch and customer identification details, along with metadata associated with loan and lead records.
The identification of personal information in the records does not, by itself, establish that customers' bank accounts or funds have been accessed or compromised.
SBI cyber incident: How the bank respondedSBI received alerts about the suspected exposure on October 16 from its threat-intelligence service provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team (CERT-In).
Following the alerts, the bank activated its cyber incident response and containment protocols. It also appointed an independent cybersecurity agency empanelled with CERT-In to investigate the incident.
The investigation is expected to establish the authenticity and extent of the information that may have been exposed, its possible source and the risks associated with the incident.
Also Read | Explained: What is Shamonda virus? WHO says first human case reported in France Is your SBI account balance safe?SBI has said the incident has had no material impact on its core business operations, financial performance or business continuity. The bank has also reassured customers that their account balances and funds are safe.
However, the investigation is ongoing, and the extent and implications of the suspected data exposure are yet to be fully established.
Customers should avoid sharing one-time passwords (OTPs), PINs or passwords with anyone, including callers claiming to represent the bank. They should also exercise caution with unexpected links, messages and emails requesting personal or financial information.
Customers who receive a notification from SBI should verify that it is genuine before acting on it. Any suspicious communication or suspected unauthorised transaction should be reported to the bank through its official channels.
Legal Disclaimer:
MENAFN provides the
information “as is” without warranty of any kind. We do not accept
any responsibility or liability for the accuracy, content, images,
videos, licenses, completeness, legality, or reliability of the information
contained in this article. If you have any complaints or copyright
issues related to this article, kindly contact the provider above.


Comments
No comment