


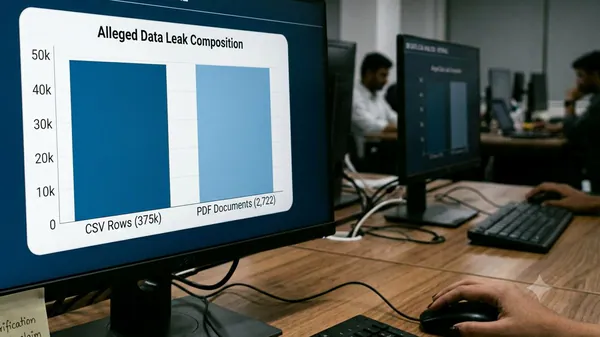
SBI Data Leak Claim: Hacker Allegedly Leaks 3.75 Lakh Records, 2,722 PDF Documents Details Remain Unverified


CyberPulse56, in a post on social media platform X, reported the alleged data leak on October 16, 2026. The claimed dataset comprises 375,000 CSV rows and 2,722 PDF documents containing personal customer information, loan applications, supporting documents, account-opening applications, addresses and other application-related details.
The threat has reportedly described it as the first release of the dataset. However, the claim does not disclose the source of the allegedly leaked information.
If the dataset attributed to Siriusim is found to be genuine and contains sensitive customer records, the information could potentially be misused for impersonation, phishing, identity theft or attempts to obtain loans fraudulently.
Cyberattacks target financial institutionsThe alleged SBI data leak claim comes amid reports of a series of cyberattacks targeting India's financial services sector.
The Economic Times reported on October 15, citing people familiar with the development, that as many as 20 financial institutions had been affected earlier in the month by a spate of cyberattacks. Funds were allegedly siphoned off using stolen credentials belonging to partner banks.
The incidents highlight the risks posed by compromised credentials and weaknesses in the systems connecting financial institutions, payment providers and digital lending platforms.
Also Read | India issues first ever AI agent cyber-attack warning. What's at stake? CERT-In warns of cyberattacks targeting fintech firms, digital lendersSeparately, the Indian Computer Emergency Response Team (CERT-In) issued an advisory on October 9 warning about multiple cyberattack campaigns targeting non-banking financial companies (NBFCs), digital lending platforms, fintech entities, payment service providers and digital wallets.
According to the advisory, attackers are compromising internet-facing applications, exposed application programming interfaces (APIs) and privileged endpoints to steal payment gateway and partner-bank credentials.
Using these credentials, threat actors directly invoke fund-transfer and disbursal APIs from within organisations' whitelisted infrastructure, bypassing safeguards such as KYC checks, loan approvals, beneficiary verification and transaction limits.
The fraudulent transactions reportedly use dummy reference identifiers and route funds to attacker-controlled mule accounts across multiple banks.
Also Read | Cyber fraud alert: How to stay safe from AI voice-cloning scams
Legal Disclaimer:
MENAFN provides the
information “as is” without warranty of any kind. We do not accept
any responsibility or liability for the accuracy, content, images,
videos, licenses, completeness, legality, or reliability of the information
contained in this article. If you have any complaints or copyright
issues related to this article, kindly contact the provider above.


Comments
No comment