


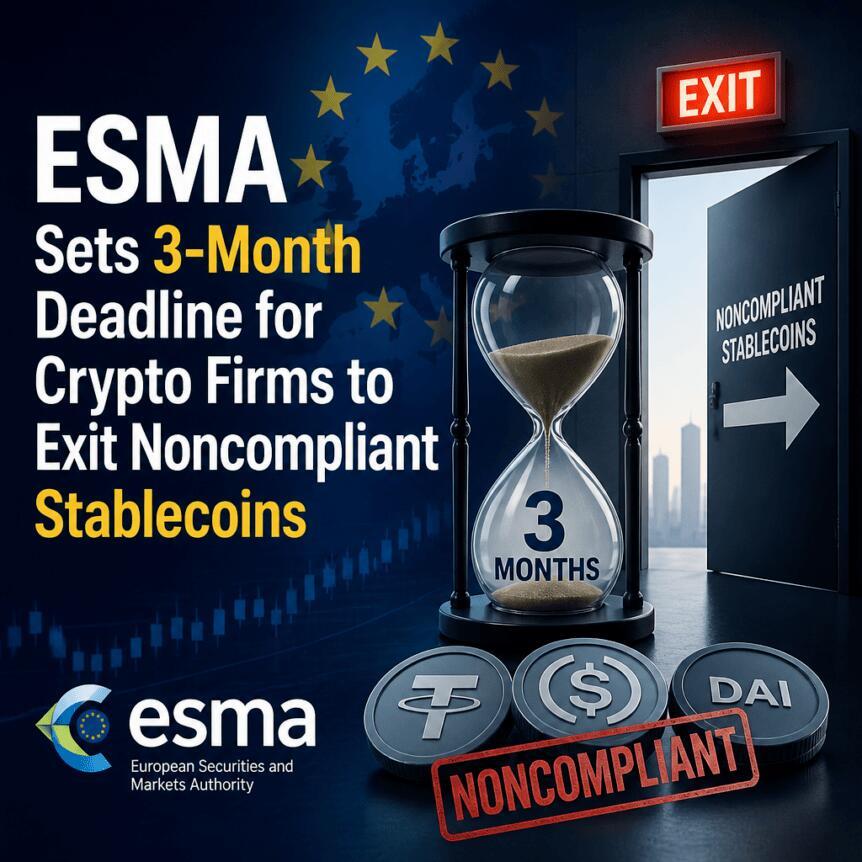
ESMA Sets 3-Month Deadline For Crypto Firms To Exit Noncompliant Stablecoins


The regulator's instructions come with a timeline: remaining exposures to non-compliant stablecoins should be dealt with no later than Jan. 8, 2027, with an expectation that action starts immediately. The move is aimed at limiting how far unauthorized stablecoins can be accessed by EU users as the MiCA regime continues to roll out.
Key takeaways- MiCA-authorized crypto-asset service providers must stop providing services related to non-MiCA-compliant stablecoins to EU clients. National regulators are expected to enforce a deadline of Jan. 8, 2027 for addressing remaining exposures. ESMA's scope includes trading, exchanges, custody, transfers, order execution, investment advice, and portfolio management. Exit-only activity may be allowed temporarily-such as liquidation or conversion-but must be closely supervised. Firms should implement technical, contractual, and organizational controls to prevent clients from increasing exposure to unauthorized tokens.
ESMA said national regulators should require crypto-asset service providers (CASPs) authorized under MiCA to cease offering services connected to stablecoins that are not compliant with the MiCA regime. The regulator's position, published on Thursday, is directed at asset-referenced tokens and e-money tokens that do not meet MiCA requirements.
ESMA's language is explicit on the operational expectation: MiCA-authorized firms should not continue providing those services to clients within the European Union. That includes the full range of regulated crypto services, rather than a narrow subset of activities.
What services are covered-and what firms must do insteadAccording to ESMA, the guidance applies to MiCA-regulated crypto services such as trading platform services, exchange services, order execution, custody and safekeeping, transfers, investment advice, and portfolio management.
ESMA also outlined what compliance should look like beyond simply stopping new customer routes. Firms are expected to put in place technical, contractual, and organizational controls designed to ensure EU clients cannot acquire additional non-authorized stablecoins or increase their exposure to them.
The regulator did acknowledge one carve-out: limited services may be permitted to help clients reduce positions already held-such as liquidation, conversion, withdrawals, transfers, and safekeeping. However, ESMA stressed that these activities must remain temporary and under close supervision. The overall direction is that the remaining pathway should be an orderly exit, not a continuation of access.
From trading restrictions to broader enforcementESMA's move builds on earlier guidance from January 2025, which Cointelegraph previously reported as calling for restrictions on trading and exchange services involving non-compliant stablecoins. This latest opinion expands the practical implications of that earlier stance by making the“stop providing services” requirement applicable across a broader set of crypto services under MiCA.
For market participants, the difference is meaningful. Trading and exchange venues often sit at the front of the customer journey, but custody, portfolio management, and investment advice can also sustain exposure even after trading access is curtailed. ESMA's update therefore pushes firms to think about the full service stack-how stablecoins enter client portfolios, how those holdings are maintained, and how transfers and safekeeping affect continuity of exposure.
Why the Jan. 8, 2027 deadline matters for EU usersThe enforcement timeline-no later than Jan. 8, 2027-signals that regulators intend to transition away from non-MiCA-compliant stablecoin access in a structured way. For investors and service users, the key risk is operational: some existing exposure may require planned conversion, liquidation, or withdrawal pathways rather than ad hoc changes once services are paused.
At the same time, ESMA's insistence on controls to prevent clients from increasing exposure suggests that firms will be expected to actively manage“access risk,” not only discontinue offerings. That may require changes to onboarding policies, token listings, transaction routing, custody rules, and portfolio tools-especially where stablecoin holdings persist through portfolio management or safekeeping services.
Until firms fully demonstrate compliance, national regulators are likely to scrutinize whether“temporary exit” measures remain limited in scope and time. ESMA's approach also raises the bar for documentation and governance, given that it links compliance expectations to multiple categories of controls: technical systems, contractual terms, and internal organizational processes.
Looking ahead, the practical question for EU market participants is how quickly service providers can redesign their product and custody flows to block new or increased exposure to unauthorized stablecoins-while still allowing supervised client exits. With the Jan. 8, 2027 date now set, attention will likely shift from policy intent to implementation details at both firm and regulator level.
Risk & affiliate notice: Crypto assets are volatile and capital is at risk. This article may contain affiliate links.
Legal Disclaimer:
MENAFN provides the
information “as is” without warranty of any kind. We do not accept any
responsibility or liability for the accuracy, content, images, videos,
licenses, completeness, legality, or reliability of the information
contained in this article. If you have any complaints or copyright issues
related to this article, kindly contact the provider above.


Comments
No comment