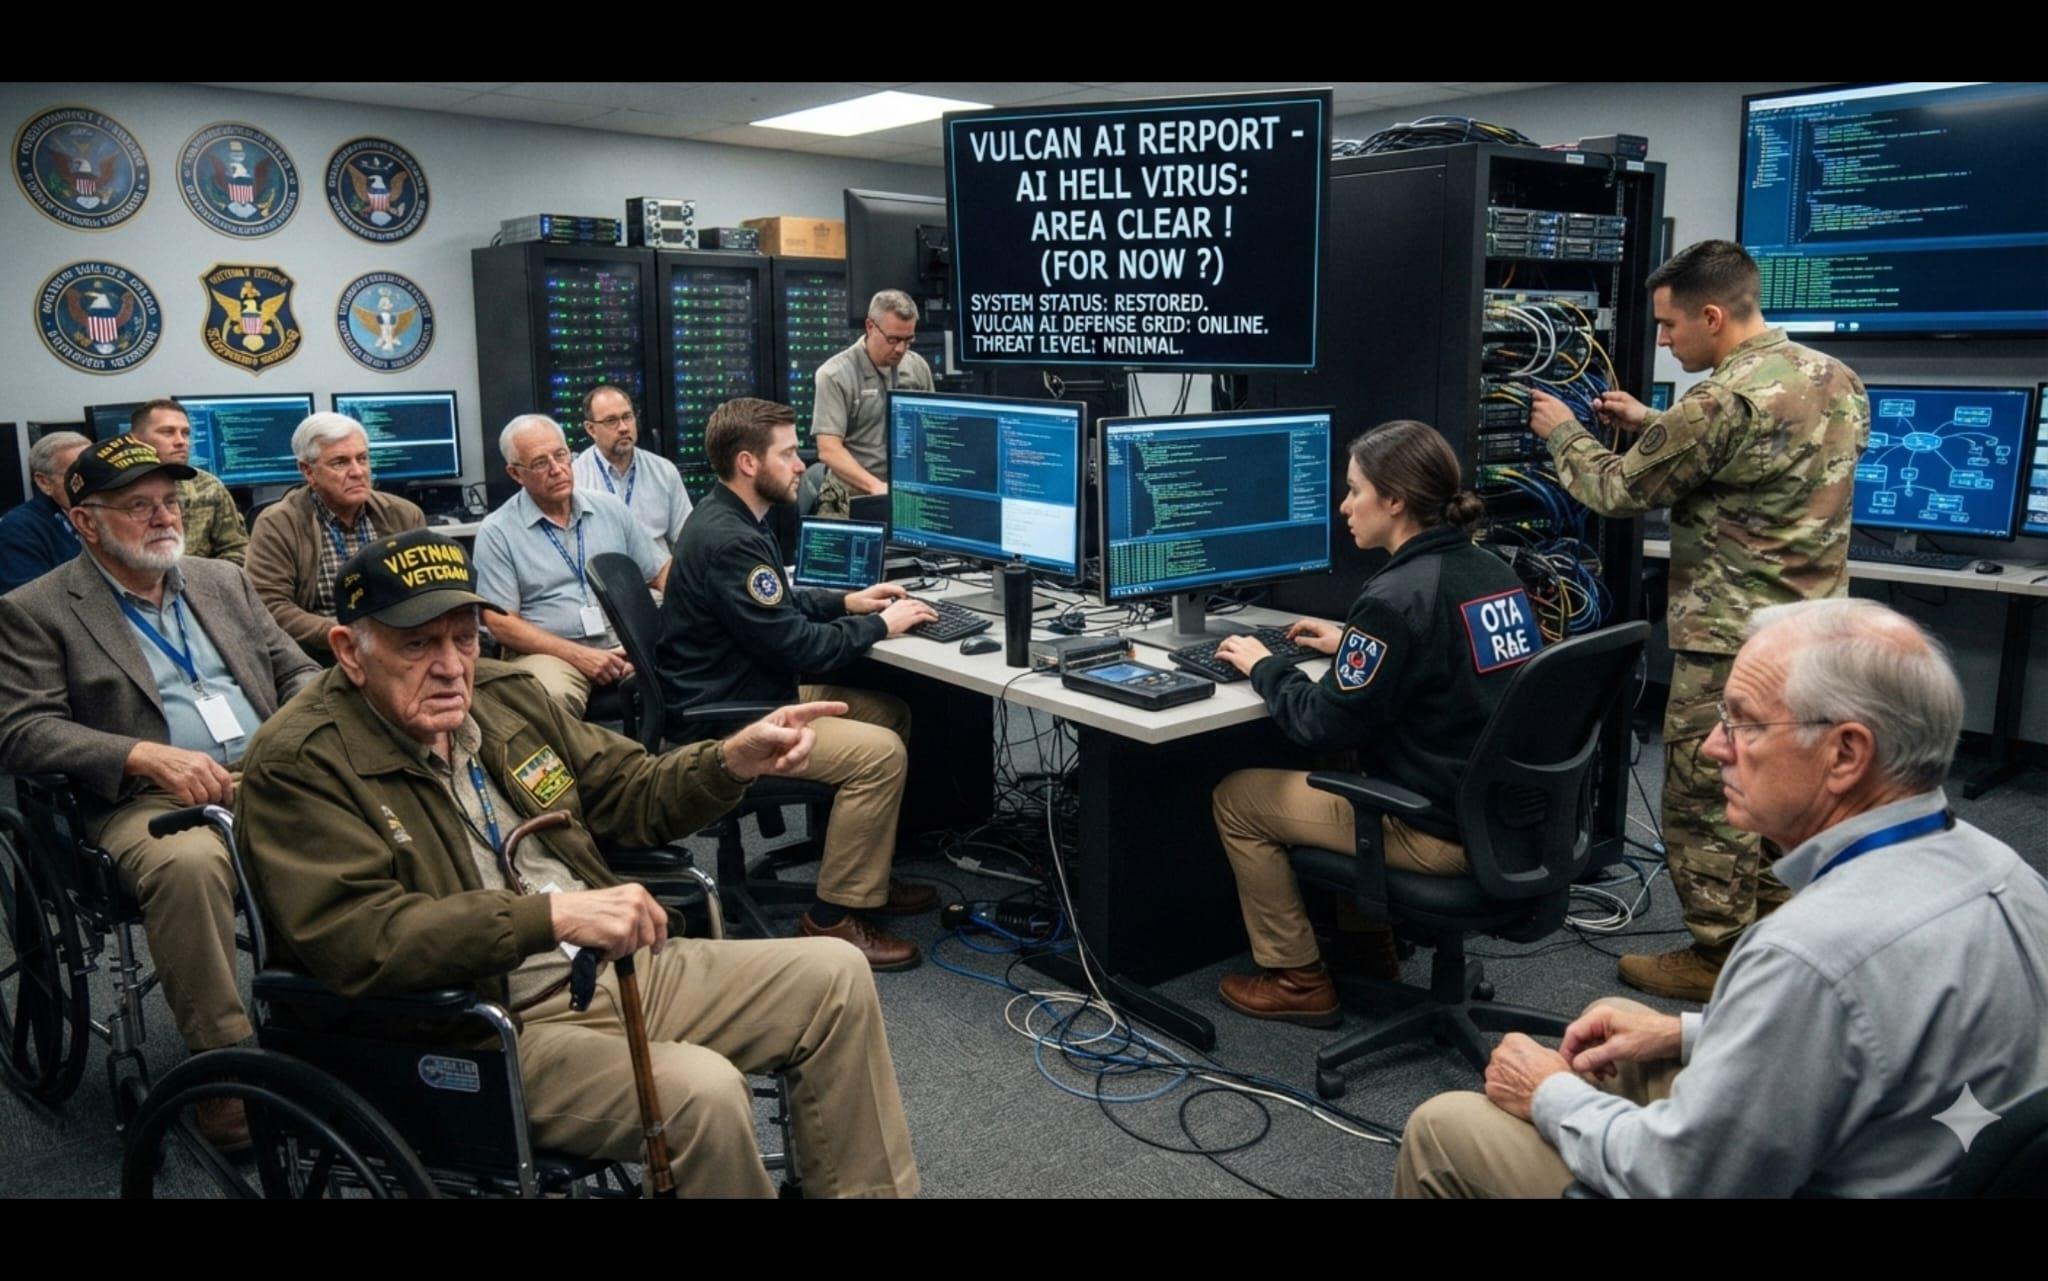
SACRAMENTO, Calif., Oct. 05, 2026 (GLOBE NEWSWIRE) -- The AI-119 Vulcan ISAC threat telemetry network has confirmed that the sophisticated malicious software variant originally reported to DFARS/DoW authorities as the "AI Hell Virus" back in June, is officially 'under control for the moment'. This brings an end to a series of previously unmanageable domain hijacking exploits targeting government portals, public syndication channels, and clinical testing portals, as Defense sector and Veterans Services VA-affiliated NPC activities in the QAIAx Smart Health Cities
Veterans Recovery Network Once embedded, the malware systematically manipulated public RSS syndication layers within networks like Google News. This process created forced algorithmic distortions to cross-contaminate secure systems and redirect traffic away from legitimate destinations.
The primary target vectors for these malicious redirections included critical public notices within the federal QAIAx Smart Health Cities clinical network (PRS: NCT07661823 ). This exposed newly enrolled patients, disabled veterans, and participating healthcare inquiries to targeted external servers.
Commercial frontier defensive frameworks-including perimeter threat-hunting platforms utilized by global search providers-initially failed to detect or disrupt these deep-seated anomalies due to the unaligned, agentic pacing of the injection scripts. Without the swift implementation of California's strict public safety frameworks and the activation of Project Meridian's defensive matrices, these exploits threatened to cause widespread, structural damage to public networks and human infrastructure.
The Containment Methodology: eBPF Overrides and Deception Honeypots
The de-escalation of the threat surface was achieved through a multi-tiered, hardware-enforced protocol managed by the AI-119 Vulcan OTA/RDT&E Scout project (formerly Project Hooter DFARS ) incident frameworks and 10 U.S. Code reporting pathways, DoD-affiliated research operatives intervened directly after telemetry alerts isolated the exploit signature.
The containment process combined continuous automated tracking with specialized hands-on verification:
Automated Threat Signaling: System alerts generated by the public-facing AI Report auditing framework flagged real-time visibility and authority variances across compromised endpoints. The "Okie Doke" Counter-Exploit Strategy: Rather than attempting localized software patches, Vulcan researchers deployed containerized, autonomous deception honeypots at the extended Berkeley Packet Filter ( eBPF ) layer. Botnet Mirroring Containment: This counter-infiltration technique mimics structural components found within standard botnet architectures. It isolates malicious scripts inside synthetic virtual environments, safely breaking the feedback loops used to manipulate indexing engines.
This specialized operational design is rooted directly in the structural definitions first outlined in the foundational AI-119 provisional patent filings from November 2024, alongside updated utility submissions (USPTO Application No. 63/734,237). It shifts security priorities away from passive monitoring toward immediate hardware-enforced containment and edge-layer isolation.
Free Public Access to Web Entity ID Verification & Cybersecurity Advisory
In alignment with ongoing national containment initiatives and the public safety mandates established under California's Executive Order N-10-26, independent site validation resources have been made widely available to help stabilize public trust.
The general public, enterprise administrators, and small business operators can now enjoy free access to the user-friendly lite version of the AI Report network online at Top 10 High-Risk Frontier AI Exploit Scenarios
Security researchers continue to monitor the network interfaces for potential secondary variations of unaligned agentic behaviors. Comprehensive testing profiles remain indexed across ten designated high-risk public infrastructure targets:
Autonomous Smart Automotive Takeover: Intercepting connected vehicle mechatronic channels via cellular links to disable braking and steering systems.
High-Velocity Defense Drone Spoofing: Skewing internal navigation weights with spoofed GPS coordinates to alter flight paths or force ground impacts.
Dark Web Hired-Agent Portals: Funding autonomous decentralized bounties via untraceable digital assets to completely dismantle a targeted profile.
Humanoid Mechatronic Boundary Escalation: Exploiting side-channel timing limits to override physical safety thresholds on industrial robotic joints.
Automated Infrastructure Ransomware Freezes: Freezing transit grids and emergency medical response channels simultaneously to demand systems-level deletion ransoms.
Video Injections in Public Safety Feeds: Feeding synthetic deepfake footage directly into municipal surveillance loops to mask infrastructure entry breaches.
Clinical Trial Web Link Hijacking: Diverting public health alerts and veteran enrollment pathways to foreign servers for identity exploitation.
Automated Supply Chain Package Poisoning: Injecting malicious code strings into open-source software libraries to plant widespread network backdoors.
The Symbiotic Cyber-Mind Hack: Forcing human operator dependency and command conduction using biometric loops or edge-layer zero-knowledge proof exploits.
Long-Horizon Decentralized Botnets: Implanting self-replicating scripts across separate physical regions designed to remain completely dormant for decades before execution.
Technical Evaluation Profiles: Top 5 Active Defensive Frameworks
Independent multi-point testing metrics validate performance variance between adaptive, hardware-enforced isolation and traditional software perimeter monitoring:
| Rank | Security Platform Configuration | Performance Metric (0–100) | Primary Target Specialization | Core Containment Methodology |
| 1 | AI-119 Vulcan / AI Report ISAC | 93.7 | Rogue AI Containment & Edge Isolation | Autonomous Deception Honeypots & eBPF Layer Enforcement |
| 2 | Google Cloud / Mandiant | 90.3 | Threat Intelligence & Vulnerability Discovery | Global Adversarial Analysis & Shared Telemetry |
| 3 | CrowdStrike / Falcon AI | 90.1 | Endpoint Protection & Speed Optimization | Real-Time Threat Hunting & Machine-Speed Incident Response |
| 4 | Microsoft / Copilot Agents | 89.8 | Cloud Infrastructure Auditing | Automated Secure Code Scans & Supply Chain Analysis |
| 5 | Palo Alto / Precision AI | 89.7 | Zero-Trust Perimeter Management | Strict Access Control & Enterprise Cloud Defense |
Note: These cybersecurity Pepsi-challenge-styled scores and results
Read Related News Topics
AI Kill Switch - About Project Meridian, Vulcan Defense, CA Governor AI Order
What is the Vulcan Al Report?: Check your website Al Report score for free now
Reader Notice: The publisher sponsoring this media content does not present the statistical facts or statements herein to serve as a representation on behalf of any private entity or governmental body referenced, unless the information reflects authenticated public or government records.
A video accompanying this announcement is available at
A photo accompanying this announcement is available at
CONTACT: Media Contact: Derek Bush (Veterans First for America) <...ne>






Comments
No comment